Thursday, 12 September 2024

Comprehensive Guide to Infrastructure Robustness Metrics

Comprehensive Guide to Infrastructure Robustness Metrics

In the world of IT infrastructure and systems management, understanding and implementing robust metrics is crucial for ensuring system reliability, performance, and resilience. This article delves into key metrics used to analyze infrastructure robustness, providing detailed explanations, examples, and insights into their criticality.

1. RPO (Recovery Point Objective)

Definition: RPO defines the maximum acceptable amount of data loss measured in time after a critical event.

Example: If a system has an RPO of 1 hour, it means that in the event of a disaster, the system can lose up to 1 hour of data without severely impacting the business.

Criticality:

  • Critical: For systems handling frequent, high-value transactions (e.g., stock trading platforms, e-commerce sites)
  • Less Critical: For systems with infrequent updates or where data loss is less impactful (e.g., internal wikis, long-term archives)

2. RTO (Recovery Time Objective)

Definition: RTO is the maximum acceptable downtime after a failure or disaster event.

Example: An RTO of 4 hours means the system should be back online and operational within 4 hours of an outage.

Criticality:

  • Critical: For systems requiring high availability (e.g., emergency services systems, core banking applications)
  • Less Critical: For non-essential systems or those with predictable low-usage periods (e.g., internal HR systems, batch processing systems)

3. MTTR (Mean Time To Recover)

Definition: MTTR measures the average time it takes to repair a failed component or system and return it to operational status.

Example: If a system experiences 5 failures in a month with recovery times of 1, 2, 3, 2, and 2 hours respectively, the MTTR would be (1+2+3+2+2) / 5 = 2 hours.

Criticality:

  • Critical: For systems where quick recovery is essential (e.g., production lines, critical infrastructure)
  • Less Critical: For redundant systems or those with less impact on core operations

4. MTBF (Mean Time Between Failures)

Definition: MTBF is the predicted elapsed time between inherent failures of a system during normal operation.

Example: If a server fails 3 times in 3000 hours of operation, its MTBF would be 3000 / 3 = 1000 hours.

Criticality:

  • Critical: For systems where failure can lead to significant financial loss or safety issues (e.g., aircraft systems, medical devices)
  • Less Critical: For systems with high redundancy or where failure impact is minimal

5. Availability

Definition: Availability is the proportion of time a system is in a functioning condition, often expressed as a percentage.

Example: If a system is operational for 8,760 hours out of a year (8,766 hours), its availability would be (8,760 / 8,766) * 100 = 99.93%.

Criticality:

  • Critical: For systems requiring constant uptime (e.g., telecommunications networks, cloud services)
  • Less Critical: For non-essential services or those with acceptable downtime windows

6. Durability

Definition: Durability refers to the probability that data will be preserved over a long period without corruption or loss.

Example: Amazon S3's standard storage class offers 99.999999999% (11 9's) durability over a given year.

Criticality:

  • Critical: For long-term data storage systems, especially those containing irreplaceable data (e.g., scientific research data, financial records)
  • Less Critical: For temporary data storage or easily reproducible data

7. SLA (Service Level Agreement) Metrics

Definition: SLA metrics are specific performance and availability guarantees made by service providers to their customers.

Example: An SLA might guarantee 99.9% uptime, a maximum response time of 200ms for API calls, or a minimum throughput of 1000 transactions per second.

Criticality:

  • Critical: For business-critical services, especially in B2B contexts where breaches can lead to penalties or lost business
  • Less Critical: For internal services or where formal agreements are not in place

8. Load Testing Metrics

Definition: Load testing metrics measure how a system performs under various levels of simulated load.

Example: A load test might reveal that a web application can handle 10,000 concurrent users with an average response time of 1.5 seconds, but degrades significantly beyond that point.

Criticality:

  • Critical: For systems expecting high or variable load (e.g., e-commerce sites during sales events, ticket booking systems)
  • Less Critical: For systems with predictable, low-volume usage

9. Failover Time

Definition: Failover time is the time it takes for a system to switch to a backup or redundant system when the primary system fails.

Example: In a high-availability database cluster, failover time might be the duration between the primary node failing and a secondary node taking over, typically measured in seconds.

Criticality:

  • Critical: For systems requiring near-zero downtime (e.g., financial trading systems, real-time monitoring systems)
  • Less Critical: For systems where brief interruptions are acceptable

10. Data Integrity Measures

Definition: Data integrity measures ensure that data remains accurate, consistent, and unaltered throughout its lifecycle, including during and after recovery processes.

Example: Checksums, error-correcting codes, and blockchain-like ledgers are examples of data integrity measures.

Criticality:

  • Critical: For systems where data accuracy is paramount (e.g., financial systems, medical records)
  • Less Critical: For systems dealing with non-sensitive or easily verifiable data

Conclusion

Understanding and implementing these metrics is crucial for building robust, reliable, and resilient IT infrastructure. The criticality of each metric can vary depending on the specific use case, industry regulations, and business requirements. By carefully considering and applying these metrics, organizations can significantly enhance their ability to prevent, respond to, and recover from various types of system failures and disasters.


https://bit.ly/3AZgkMx
https://bit.ly/3XFCOLn

https://guptadeepak.com/content/images/2024/09/Infrastructure-deepak-gupta.webp
https://guptadeepak.weebly.com/deepak-gupta/comprehensive-guide-to-infrastructure-robustness-metrics

Monday, 2 September 2024

Demystifying SOC 2 Compliance for Startups: A Simple Guide

Demystifying SOC 2 Compliance for Startups: A Simple Guide

This article provides a comprehensive overview of SOC2 compliance for technology startups, particularly those with fewer than 10 employees. It aims to demystify the SOC2 certification process, highlight its benefits, and offer cost-effective strategies for achieving compliance.

The article emphasizes practical, actionable steps that startups can take to prepare for and implement SOC2 policies without significant financial burden.

What is SOC2?

SOC2 (Service Organization Control 2) is a auditing procedure developed by the American Institute of CPAs (AICPA) to ensure that service providers securely manage data to protect the interests of their organization and the privacy of their clients.

SOC2 defines criteria for managing customer data based on five "trust service principles"—security, availability, processing integrity, confidentiality, and privacy.

SOC2 Type 1 vs Type 2

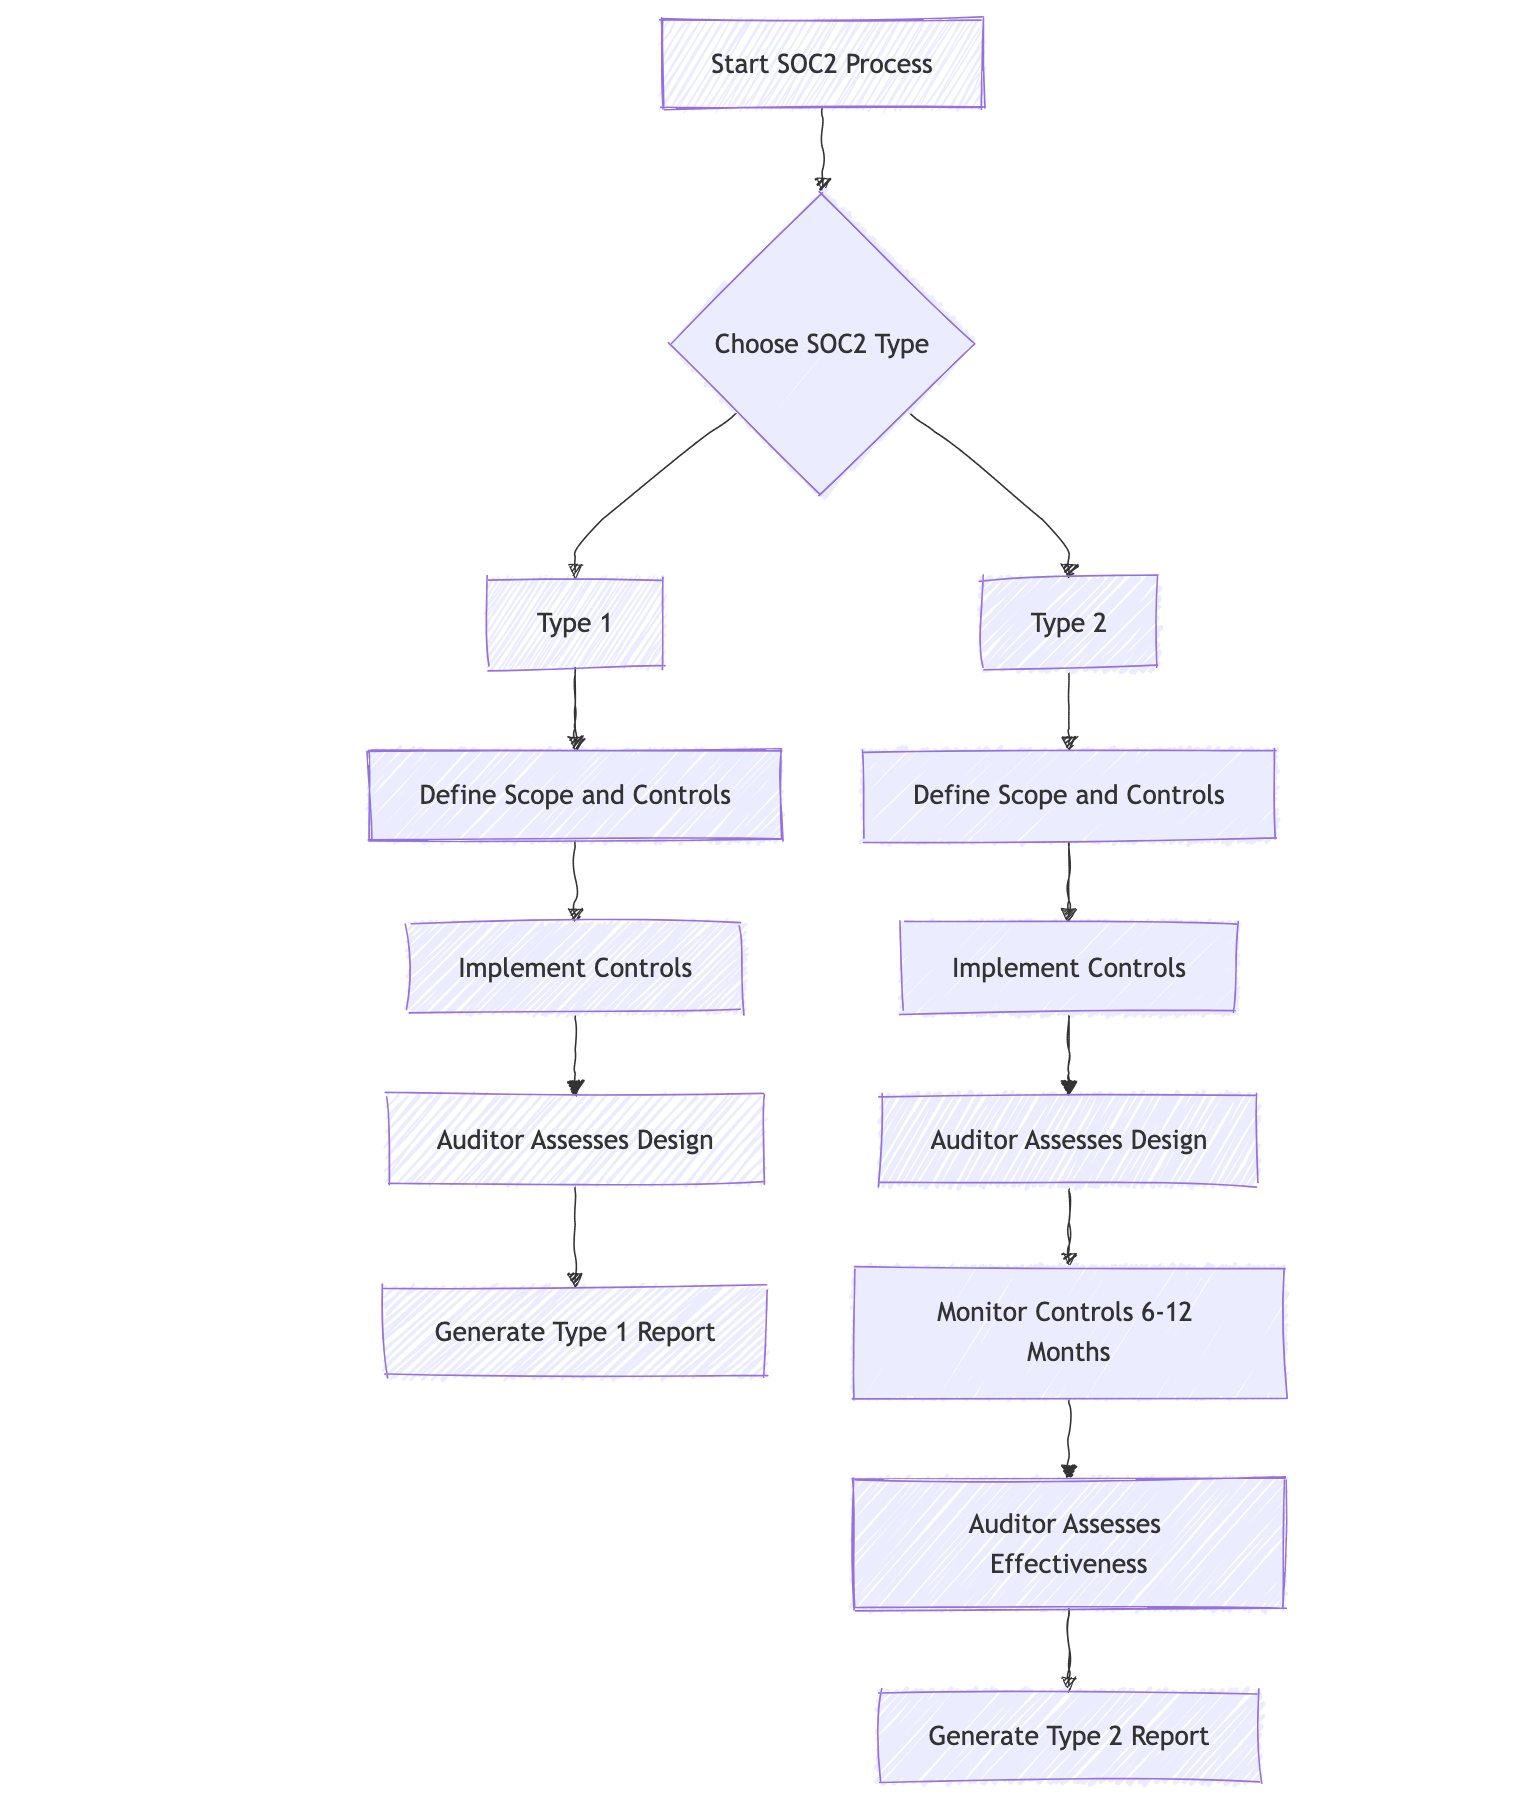
Understanding the difference between SOC2 Type 1 and Type 2 reports is crucial for organizations pursuing SOC2 compliance. Both types of reports assess an organization's internal controls, but they differ in scope and duration of examination.

SOC2 Type 1:

  • Assesses the design of controls at a specific point in time
  • Provides a snapshot of the organization's security posture
  • Typically faster and less expensive to obtain
  • Useful for organizations just starting their compliance journey

SOC2 Type 2:

  • Assesses both the design and operating effectiveness of controls over a period of time (usually 6-12 months)
  • Provides a more comprehensive view of the organization's security practices
  • More rigorous and time-consuming
  • Generally considered more valuable by clients and partners
Demystifying SOC 2 Compliance for Startups: A Simple Guide

Key Benefits of SOC2 Compliance

  1. Enhanced Security Posture: Implementing SOC2 controls strengthens overall security practices.
  2. Competitive Advantage: Compliance can be a differentiator in the market.
  3. Customer Trust: SOC2 certification builds credibility with clients and partners.
  4. Risk Management: The process helps identify and mitigate potential security risks.
  5. Operational Efficiency: Standardized processes often lead to improved operations.
  6. Regulatory Alignment: SOC2 can help meet requirements for other regulations (e.g., GDPR, HIPAA).

How it works for SaaS companies

For SaaS companies, SOC2 compliance demonstrates a commitment to data security and privacy. It involves:

  1. Selecting the relevant trust service principles
  2. Implementing controls and processes to meet these principles
  3. Undergoing an audit by a certified public accountant
  4. Receiving a SOC2 report detailing the effectiveness of these controls

Step-by-step Approach

Demystifying SOC 2 Compliance for Startups: A Simple Guide
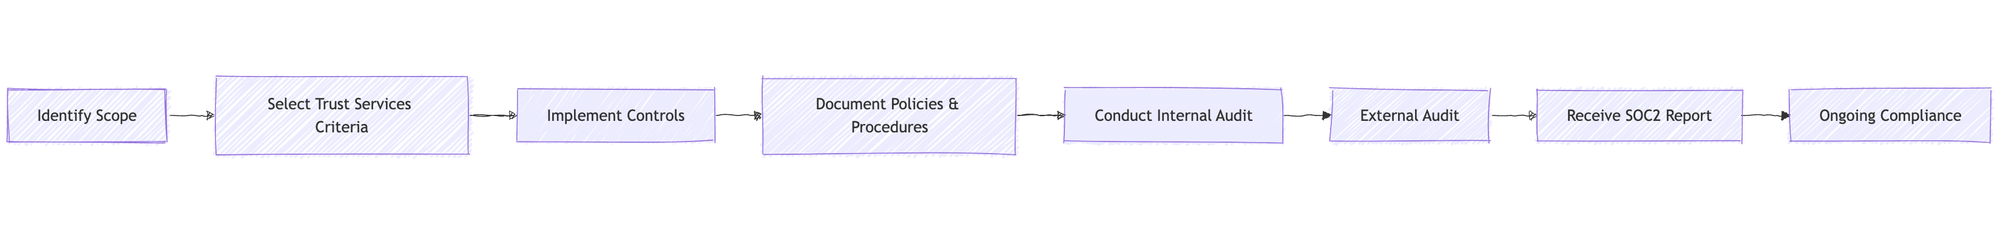
  1. Identify Scope: Determine which systems, data, and processes will be covered by the SOC2 audit.
  2. Select Trust Services Criteria: Choose which of the five trust principles (Security, Availability, Processing Integrity, Confidentiality, and Privacy) are relevant to your business.
  3. Implement Controls: Put in place the necessary technical and organizational measures to meet the selected criteria.
  4. Document Policies & Procedures: Create and maintain documentation of all relevant security policies and procedures.
  5. Conduct Internal Audit: Perform a self-assessment to ensure readiness for the external audit.
  6. External Audit: An independent auditor evaluates your systems and controls against the SOC2 criteria.
  7. Receive SOC2 Report: Upon successful completion of the audit, receive the official SOC2 report.
  8. Ongoing Compliance: Continuously monitor and maintain compliance with SOC2 standards.

SOC2 Compliance for Startups

Challenges and Opportunities

Startups face unique challenges in achieving SOC2 compliance:

  • Limited resources (both financial and personnel)
  • Lack of dedicated security staff
  • Rapidly changing business environment

However, they also have opportunities:

  • Ability to build security into the core of operations from the start
  • Flexibility to implement new processes quickly
  • Potential for faster decision-making and implementation
Demystifying SOC 2 Compliance for Startups: A Simple Guide
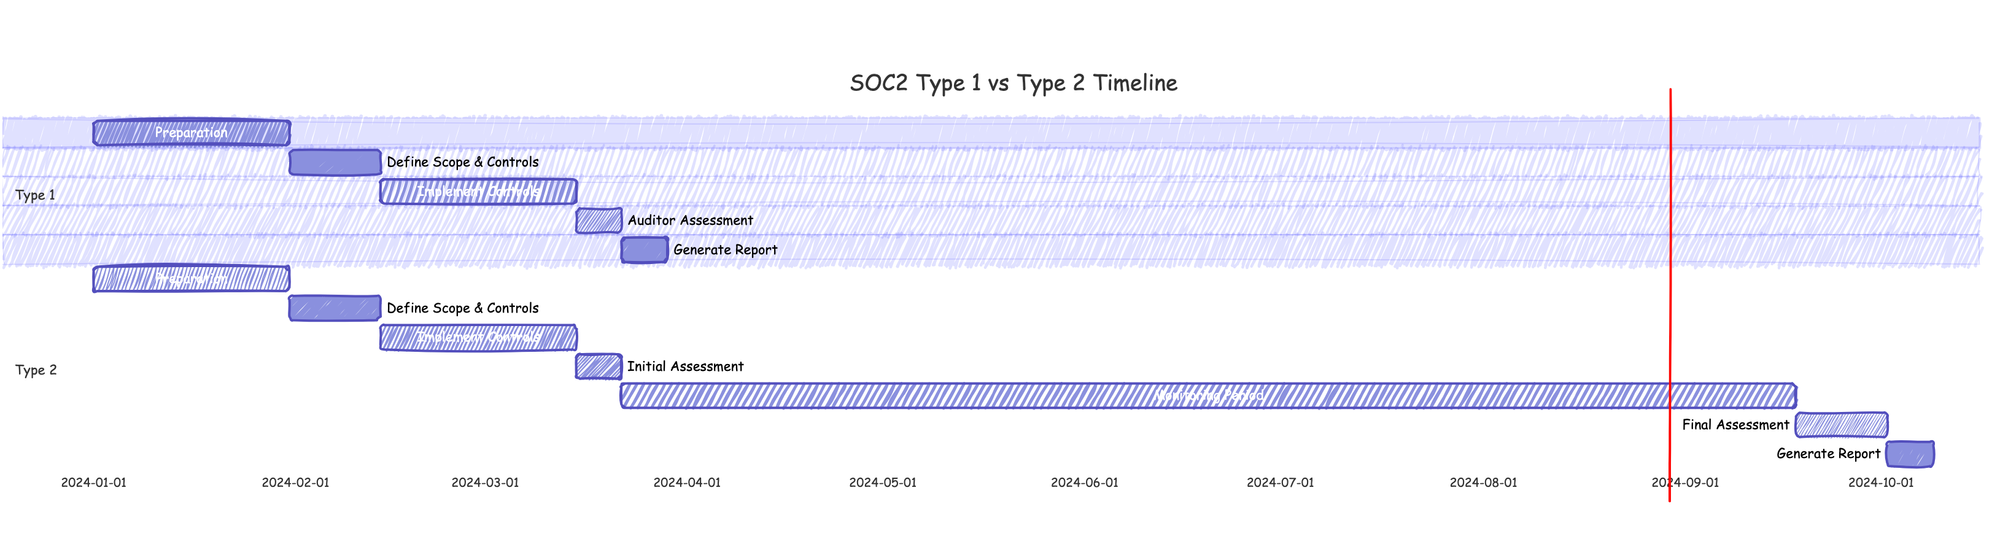
Sample timeline for SOC2 Type1 and Type2

Required vs. Optional Policies

SOC2 is based on the Trust Services Criteria (TSC), which include:

  1. Security (required)
  2. Availability (optional)
  3. Processing Integrity (optional)
  4. Confidentiality (optional)
  5. Privacy (optional)
Principle Required/Optional Description
Security Required Protection against unauthorized access
Availability Optional System availability for operation and use
Processing Integrity Optional System processing is complete, accurate, timely, and authorized
Confidentiality Optional Information designated as confidential is protected
Privacy Optional Personal information is collected, used, retained, and disclosed in conformity with commitments

For startups, focusing on the required Security principle and selectively adding others based on business needs is often the most practical approach.

Cost-Effective SOC2 Compliance Strategies

Policy Implementation

  1. Start with a Gap Analysis: Identify what controls you already have in place and what needs to be implemented.
  2. Prioritize Critical Policies: Focus on essential security policies first.
  3. Leverage Existing Frameworks: Use established frameworks like NIST or ISO 27001 as a starting point.
  4. Document as You Go: Integrate documentation into your daily processes to avoid last-minute rushes.
  5. Automate Where Possible: Use tools to automate policy enforcement and evidence collection.

Free and Open Source Tools

Category Tool Description
Vulnerability Scanning OpenVAS Comprehensive vulnerability scanner
Intrusion Detection Snort Network intrusion detection system
Log Management ELK Stack (Elasticsearch, Logstash, Kibana) Log collection, analysis, and visualization
Access Control OpenLDAP Open-source implementation of LDAP protocol
Encryption VeraCrypt Disk encryption software
Password Management KeePass Free, open-source password manager
Network Monitoring Nagios Network and infrastructure monitoring

Policy Preparation and Implementation Guide

  1. Information Security Policy
    • Template: NIST Special Publication 800-53
    • Implementation: Use NIST guidelines to create a comprehensive security policy. Ensure all employees read and acknowledge the policy.
  2. Access Control Policy
    • Template: CIS Controls v8
    • Implementation: Use OpenLDAP for centralized user management. Implement multi-factor authentication using free tools like Google Authenticator.
  3. Change Management Policy
    • Template: ITIL Change Management
    • Implementation: Use a free project management tool like Trello or Jira to track and approve changes.
  4. Incident Response Plan
  5. Risk Assessment Process
  6. Vendor Management Policy
  7. Data Classification Policy
  8. Business Continuity and Disaster Recovery Plan

Conclusion

Achieving SOC2 compliance is a significant undertaking, but it's not out of reach for small technology startups. By focusing on the essential security principle, leveraging free and open-source tools, and implementing cost-effective strategies, startups can build a robust security posture that meets SOC2 requirements.

Remember, SOC2 compliance is an ongoing process, not a one-time achievement. Regular reviews and updates of your policies and procedures are crucial to maintaining compliance and ensuring the security of your systems and data.

By following the guidelines and using the resources provided in this report, small startups can embark on their SOC2 compliance journey with confidence, enhancing their security posture and building trust with their clients and partners.


https://bit.ly/47ixvVx
https://bit.ly/3Z4WU33

https://guptadeepak.com/content/images/2024/08/SOC2-Compliance.webp
https://guptadeepak.weebly.com/deepak-gupta/demystifying-soc-2-compliance-for-startups-a-simple-guide

Monday, 26 August 2024

Bootstrapping Growth: How B2B SaaS Startups Can Thrive on a Shoestring Budget

Bootstrapping Growth: How B2B SaaS Startups Can Thrive on a Shoestring Budget

Startups often face a critical challenge: how to achieve significant growth with limited financial resources. This is where the concept of "bootstrapping growth" comes into play. By leveraging creativity, hustle, and strategic thinking, startups can build a solid foundation for growth without relying on substantial outside investment. This article delves deep into the strategies and tactics that can help B2B SaaS startups bootstrap their way to success.

Understanding Bootstrapped Growth

Bootstrapped growth refers to the process of growing a business using minimal financial resources, often relying on the founder's personal savings, revenue generated from early customers, and creative, low-cost growth strategies. For B2B SaaS startups, this approach offers several advantages:

  1. Maintains equity and control for founders
  2. Forces a focus on profitability and sustainable growth
  3. Encourages creativity and resourcefulness in problem-solving
  4. Builds a lean, efficient company culture from the start

However, bootstrapping also presents unique challenges, particularly in the highly competitive SaaS space where well-funded competitors can outspend you on marketing and development. To overcome these challenges, startups need to be strategic, resourceful, and laser-focused on activities that drive real value.

Key Strategies for Bootstrapping B2B SaaS Growth

1. Leverage Free and Low-Cost Marketing Tools

In the early stages, every dollar counts. Fortunately, there's a wealth of free and low-cost tools available that can help startups punch above their weight class:

  • Content Marketing: Use tools like WordPress (free), Canva (freemium), and Unsplash (free) to create and distribute high-quality content.
  • Email Marketing: Leverage platforms like Mailchimp (free up to 2,000 contacts) or Brevo (free up to 300 emails per day) for email campaigns.
  • Social Media Management: Use Buffer (free plan available) or Adobe Express (limited free plan) to manage and schedule social media posts.
  • SEO: Utilize free tools like Google Search Console, Google Analytics, and Ubersuggest for keyword research and site optimization.
  • Customer Relationship Management (CRM): Start with HubSpot CRM (free) or Freshsales (free tier available) to manage customer relationships.

2. Focus on Organic Growth Channels

Paid advertising can quickly drain a startup's limited resources. Instead, focus on organic growth channels that require time and effort but minimal financial investment:

  • Content Marketing: Create in-depth, valuable content that addresses your target audience's pain points. This could include blog posts, whitepapers, eBooks, and case studies.
  • SEO: Optimize your website and content for search engines to drive organic traffic. Focus on long-tail keywords relevant to your niche.
  • Social Media: Build a presence on platforms where your target audience is active. Share valuable content, engage in conversations, and build relationships.
  • Community Building: Create or participate in online communities (e.g., Slack groups, LinkedIn groups, Reddit) where your target audience gathers.
  • Open-Source Strategy: If applicable, consider open-sourcing part of your product to build credibility and attract developers.

3. Implement Growth Hacking Techniques

Growth hacking involves using creative, low-cost strategies to acquire and retain customers. Some effective techniques for B2B SaaS startups include:

  • Product Hunt Launch: Orchestrate a well-planned launch on Product Hunt to gain initial traction and feedback.
  • Referral Programs: Implement a referral system that incentivizes current users to bring in new customers.
  • Strategic Partnerships: Partner with complementary businesses to cross-promote each other's products.
  • Freemium Model: Offer a free tier of your product to attract users and upsell them to paid plans.
  • Micro-Influencer Collaborations: Partner with niche influencers in your industry for product reviews or guest content.

4. Optimize for Customer Success and Retention

In B2B SaaS, retaining and expanding existing accounts is often more cost-effective than acquiring new customers. Focus on:

  • Onboarding: Create a frictionless onboarding process that quickly demonstrates value to new users.
  • Customer Education: Develop comprehensive documentation, tutorials, and webinars to help users get the most out of your product.
  • Proactive Support: Use tools like Freshdesk (freemium) to provide real-time chat support and proactively reach out to users who may need assistance.
  • Feature Adoption Campaigns: Use in-app messaging and email campaigns to drive adoption of key features that improve stickiness.

5. Leverage Data and Analytics

Data-driven decision-making is crucial for efficient growth. Use free or low-cost analytics tools to gain insights:

  • Google Analytics: Track website traffic and user behavior.
  • Mixpanel: Offers a free plan for basic product analytics.
  • Amplitude: Provides a generous free tier for event-based analytics.
  • Hotjar: Offers limited free heatmaps and session recordings.

Use these tools to identify which strategies are working, where users are dropping off, and what features are driving the most value.

6. Automate and Optimize Processes

Automation can help a small team punch above its weight. Look for opportunities to automate repetitive tasks:

  • Zapier: Automate workflows between different apps (free plan available).
  • IFTTT: Create simple automated actions (free).

7. Build in Public

"Building in public" involves sharing your startup journey openly, including successes, failures, and learnings. This approach can:

  • Generate interest and build an audience
  • Attract potential customers and partners
  • Provide valuable feedback on your product and direction

Use platforms like Twitter, LinkedIn, or a company blog to share regular updates, metrics, and behind-the-scenes insights.

8. Leverage Your Network

Your professional network can be a powerful asset for bootstrapped growth:

  • Reach out to former colleagues or classmates who might benefit from your product.
  • Ask for introductions to potential customers or partners.
  • Seek mentorship from experienced entrepreneurs in your network.

9. Focus on a Niche

Instead of trying to serve a broad market, focus on a specific niche where you can quickly establish authority and product-market fit. This allows you to:

  • Tailor your product more effectively to specific needs
  • Build a reputation as a specialist in your niche
  • Reduce marketing costs by targeting a more defined audience

10. Prioritize Revenue-Generating Activities

With limited resources, it's crucial to focus on activities that directly contribute to revenue growth:

  • Prioritize features that will help close deals with paying customers.
  • Focus on marketing activities with a clear ROI.
  • Consider offering services (consulting, implementation) alongside your product to generate additional revenue.

Case Study: Bootstrapping Success

To illustrate these principles in action, let's look at the example of Basecamp (37signals). The company bootstrapped its way to success by:

  1. Starting as a web design firm to generate revenue
  2. Building tools to solve their own problems, which became their products
  3. Focusing on a simple, opinionated product that solved a clear pain point
  4. Leveraging content marketing through their popular blog
  5. Maintaining a small, efficient team
  6. Prioritizing profitability over rapid growth

By following these principles, Basecamp grew to over $250 million in annual recurring revenue without ever taking significant outside investment.

Challenging, but Possible

Bootstrapping growth for a B2B SaaS startup is challenging but entirely possible with the right strategies and mindset. By focusing on low-cost, high-impact activities, leveraging available tools and resources, and prioritizing customer value and revenue generation, startups can build a solid foundation for growth without relying on external funding. Remember, the key is to stay lean, be creative, and always focus on providing value to your customers. With persistence and smart execution, bootstrapped startups can compete effectively in the B2B SaaS market and build sustainable, profitable businesses.


https://bit.ly/3AFQI7q
https://bit.ly/4e1T3rN

https://guptadeepak.com/content/images/2024/08/bootstrapping-growth.webp
https://guptadeepak.weebly.com/deepak-gupta/bootstrapping-growth-how-b2b-saas-startups-can-thrive-on-a-shoestring-budget

Thursday, 22 August 2024

Comprehensive Guide to API Error Code Management

Comprehensive Guide to API Error Code Management

Error handling is a critical aspect of API design and development. Well-designed error codes and messages can significantly improve the developer experience, reduce support overhead, and enhance the overall quality of your API. This guide will walk you through the best practices for creating and managing error codes in a developer-oriented API system.

Best Practices for API Error Codes

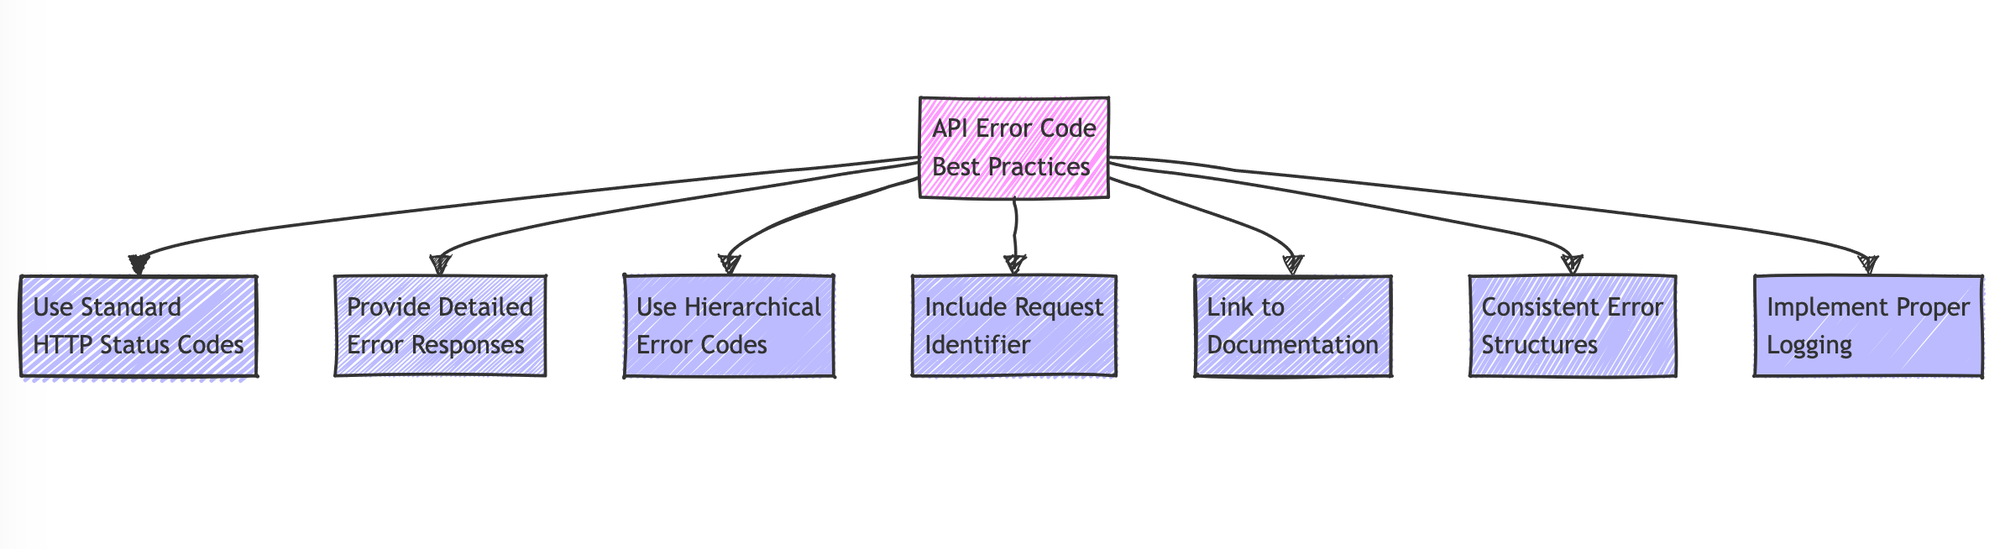
a. Use Standard HTTP Status Codes

Always use standard HTTP status codes as the first line of error reporting. These are widely understood and provide a broad categorization of the error.

HTTP/1.1 404 Not Found

b. Provide Detailed Error Responses

Include a detailed error response in the body of your HTTP response. This should be a structured object (typically JSON) containing more specific information about the error.

{  "error": {    "code": "RESOURCE_NOT_FOUND",    "message": "The requested resource could not be found.",    "details": "User with ID 12345 does not exist in the system.",    "timestamp": "2023-08-09T14:30:00Z",    "request_id": "f7a8b9c0-d1e2-3f4g-5h6i-7j8k9l0m1n2o"  }}

c. Use Hierarchical Error Codes

Implement a hierarchical error code system. This allows for both broad and specific error categorization.

Example:

  • AUTH_ERROR
    • AUTH_INVALID_CREDENTIALS
    • AUTH_EXPIRED_TOKEN
    • AUTH_INSUFFICIENT_PERMISSIONS

d. Include a Request Identifier

A Request Identifier, often called a Request ID, is a unique string or number assigned to each API request. Always include a unique identifier for each request. Its primary purpose is to provide a way to track and correlate requests across systems, which is incredibly useful for debugging, logging, and monitoring.

Example of Request Identifier in an API response:

{  "data": {    "user_id": 12345,    "username": "johndoe"  },  "meta": {    "request_id": "550e8400-e29b-41d4-a716-446655440000"  }}

Examples of Request Identifiers:

Hierarchical identifier (for microservices):

gateway-123:auth-456:user-789

Combination of service name and random number:

API-789456123

Base64-encoded random string:

dGhpc2lzYW5leGFtcGxl

Timestamp-based identifier:

20230809-154322-789

This combines a date (20230809), time (154322), and a random number (789).

UUID (Universally Unique Identifier):

550e8400-e29b-41d4-a716-446655440000

This is a common format due to its uniqueness and standardization.

Include links to relevant documentation in your error responses. This can help developers quickly find information on how to resolve the error.

{  "error": {    "code": "RATE_LIMIT_EXCEEDED",    "message": "You have exceeded your rate limit.",    "documentation_url": "https://api.example.com/docs/errors/rate-limiting"  }}

f. Use Consistent Error Structures

Maintain a consistent structure for all error responses across your API. This predictability helps developers in handling errors programmatically.

g. Implement Proper Logging

Ensure comprehensive logging on the server-side. While the client receives a sanitized error message, log detailed error information server-side for debugging and monitoring.

Things to Avoid

a. Exposing Sensitive Information

Never include sensitive information like stack traces, server paths, or database queries in error responses.

b. Using Ambiguous Error Codes

Avoid generic error codes like "ERROR_001". These provide no context and make debugging difficult.

c. Inconsistent Naming Conventions

Don't mix naming conventions. Stick to one style (e.g., UPPER_SNAKE_CASE) for all error codes.

d. Changing Error Codes Frequently

Changing error codes can break client integrations. Avoid changing existing error codes unless absolutely necessary.

Making It Developer-Friendly

a. Provide Clear and Actionable Error Messages

Error messages should clearly state what went wrong and, if possible, how to fix it.

{  "error": {    "code": "INVALID_PARAMETER",    "message": "The 'email' parameter is invalid.",    "details": "Please provide a valid email address in the format user@example.com."  }}

b. Offer Multiple Languages

Consider providing error messages in multiple languages. Use content negotiation to determine the appropriate language.

c. Implement Retry-After Headers

For rate limiting or temporary server issues, include a Retry-After header to indicate when the client should retry the request.

HTTP/1.1 429 Too Many RequestsRetry-After: 30

d. Provide SDK Support

Develop SDKs for popular programming languages that handle error parsing and provide language-specific exceptions.

Future-Proofing Your Error Codes

a. Use Versioning

Implement versioning in your API, including error responses. This allows you to evolve your error handling without breaking existing integrations.

b. Design for Extensibility

Structure your error responses to allow for easy addition of new fields in the future.

{  "error": {    "code": "PAYMENT_FAILED",    "message": "The payment could not be processed.",    "details": {      "reason": "Insufficient funds",      "transaction_id": "1234567890"    },    "additional_info": {}  // Placeholder for future extensions  }}

c. Implement Feature Flags

Use feature flags to gradually roll out changes to error handling, allowing for easy rollback if issues arise.

Examples from Industry Leaders

Stripe

Stripe's API is renowned for its developer-friendly error handling:

  • They use standard HTTP status codes.
  • Error types are clearly categorized (e.g., card_error, validation_error).
  • Detailed error messages and suggestions are provided.
  • They include a unique error ID for tracking.

Example Stripe error:

{  "error": {    "code": "resource_missing",    "doc_url": "https://stripe.com/docs/error-codes/resource-missing",    "message": "No such customer: cus_12345",    "param": "customer",    "type": "invalid_request_error"  }}

b. GitHub

GitHub's API error responses are clear and actionable:

  • They use a consistent error object structure.
  • Error messages are human-readable and often suggest a solution.
  • They provide links to relevant documentation.

Example GitHub error:

{  "message": "Validation Failed",  "errors": [    {      "resource": "Issue",      "field": "title",      "code": "missing_field"    }  ],  "documentation_url": "https://docs.github.com/rest/reference/issues#create-an-issue"}

Implementing Error Codes

a. Define an Error Code Enum

Create an enumeration of all possible error codes. This ensures consistency and makes it easier to manage codes.

from enum import Enumclass ErrorCode(Enum):    RESOURCE_NOT_FOUND = "RESOURCE_NOT_FOUND"    INVALID_REQUEST = "INVALID_REQUEST"    RATE_LIMIT_EXCEEDED = "RATE_LIMIT_EXCEEDED"    INTERNAL_SERVER_ERROR = "INTERNAL_SERVER_ERROR"    # ... more error codes ...

b. Create an Error Response Class

Implement a class to generate consistent error responses:

from dataclasses import dataclassfrom typing import Optional, Anyimport timeimport uuid@dataclassclass ErrorResponse:    code: ErrorCode    message: str    details: Optional[str] = None    timestamp: float = time.time()    request_id: str = str(uuid.uuid4())    additional_info: dict = field(default_factory=dict)    def to_dict(self) -> dict:        return {            "error": {                "code": self.code.value,                "message": self.message,                "details": self.details,                "timestamp": self.timestamp,                "request_id": self.request_id,                "additional_info": self.additional_info            }        }

c. Implement Error Handling in Your API

Use the ErrorResponse class in your API endpoints:

from fastapi import FastAPI, HTTPExceptionfrom fastapi.responses import JSONResponseapp = FastAPI()@app.exception_handler(HTTPException)async def http_exception_handler(request, exc):    error_response = ErrorResponse(        code=ErrorCode.RESOURCE_NOT_FOUND if exc.status_code == 404 else ErrorCode.INTERNAL_SERVER_ERROR,        message=str(exc.detail),        details=f"An error occurred while processing the request: {exc.detail}"    )    return JSONResponse(status_code=exc.status_code, content=error_response.to_dict())@app.get("/users/{user_id}")async def get_user(user_id: int):    # Simulating a user not found scenario    if user_id == 0:        raise HTTPException(status_code=404, detail="User not found")    # ... rest of the function ...

This setup ensures that all errors are consistently formatted and contain the necessary information for debugging and client-side error handling.

Conclusion

Implementing a robust error handling system is crucial for creating a developer-friendly API. By following these best practices, avoiding common pitfalls, and learning from industry leaders, you can create an API that is not only powerful but also a joy for developers to work with. Remember, good error handling is an ongoing process – continuously gather feedback from your API consumers and iterate on your error reporting to provide the best possible developer experience.


https://bit.ly/3SVDXfm
https://bit.ly/4dPekVk

https://guptadeepak.com/content/images/2024/08/Screenshot-2024-08-09-at-11.47.39-AM.png
https://guptadeepak.weebly.com/deepak-gupta/comprehensive-guide-to-api-error-code-management

Monday, 19 August 2024

Fuel Your B2B SaaS Startup's Growth: 6 Essential Channels

Fuel Your B2B SaaS Startup's Growth: 6 Essential Channels

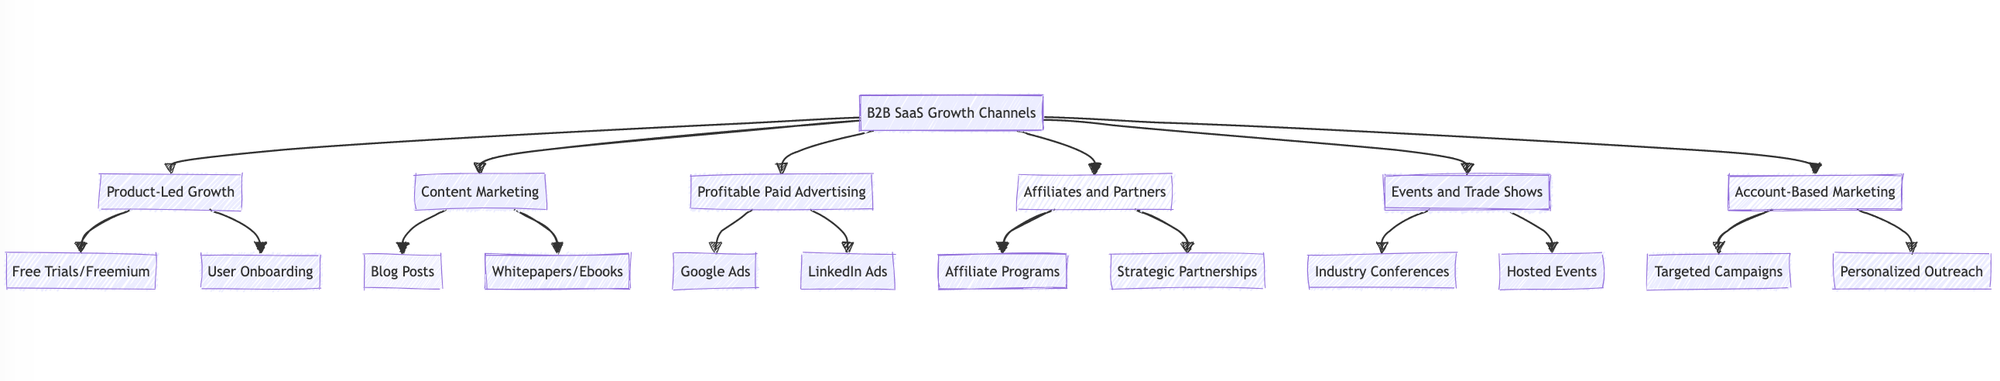
In the competitive world of B2B SaaS, choosing the right growth channels can make or break a startup. Here are six effective channels that have propelled many tech startups to success:

  1. Product-Led Growth (PLG)
  2. Content Marketing
  3. Profitable Paid Advertising
  4. Affiliates and Partners
  5. Events and Trade Shows
  6. Account-Based Marketing (ABM)

1. Product-Led Growth (PLG)

PLG puts the product at the forefront of customer acquisition and retention. It allows users to experience value before committing to a purchase, often through freemium models or free trials.

How tech startups can use PLG:

  • Offer a free tier or trial of your product
  • Focus on user onboarding and activation
  • Use in-product messaging to guide users to value
  • Implement viral loops and referral programs
  • Analyze user behavior to identify conversion triggers

Example: Slack's freemium model allowed teams to try the product before purchasing, leading to rapid adoption and organic growth.

2. Content Marketing

Content marketing establishes thought leadership and builds trust with potential customers by providing valuable, relevant content.

How tech startups can use content marketing:

  • Create a blog with industry insights and best practices
  • Develop whitepapers, ebooks, and case studies
  • Leverage SEO to improve organic visibility
  • Use social media to distribute content and engage with audience
  • Host webinars and podcasts

Example: HubSpot's comprehensive inbound marketing resources attracted and educated prospects, establishing them as industry leaders.

3. Profitable Paid Advertising

Paid advertising can quickly drive targeted traffic and leads, but it's crucial to focus on profitability.

How tech startups can use paid advertising:

  • Start with small budgets and test different platforms (Google Ads, LinkedIn, Facebook)
  • Focus on high-intent keywords and audiences
  • Create compelling ad copy and landing pages
  • Implement retargeting campaigns
  • Continuously optimize for ROI

Example: Intercom used targeted LinkedIn ads to reach decision-makers in their ideal customer profile, driving qualified leads.

4. Account-Based Marketing (ABM)

ABM focuses on targeting and engaging specific high-value accounts with personalized marketing efforts.

How tech startups can use ABM:

  • Identify and prioritize target accounts
  • Create personalized content and campaigns for each account
  • Use intent data to time your outreach
  • Align sales and marketing efforts for coordinated engagement
  • Leverage tools like LinkedIn Sales Navigator for account-based advertising

Example: Snowflake used ABM to target enterprise accounts, creating tailored content and experiences for each prospect.

5. Affiliates and Partners

Leveraging affiliates and partners can extend your reach and credibility in the market.

How tech startups can use affiliates and partners:

  • Develop an affiliate program with attractive commissions
  • Form strategic partnerships with complementary businesses
  • Create co-marketing initiatives with partners
  • Offer integration capabilities to become part of larger ecosystems
  • Participate in partner marketplaces (e.g., Salesforce AppExchange)

Example: Shopify's partner program incentivizes web developers and agencies to recommend and build on their platform.

6. Events and Trade Shows

While often considered traditional, events and trade shows can be powerful for B2B networking and lead generation.

How tech startups can use events and trade shows:

  • Attend industry-specific conferences and exhibitions
  • Host your own user conferences or meetups
  • Sponsor relevant events to increase brand visibility
  • Deliver keynote speeches or participate in panel discussions
  • Use event networking apps to schedule meetings with potential clients

Example: Salesforce's Dreamforce conference has become a major industry event, showcasing their products and fostering community engagement.

The Power of PLG and Content Marketing in Early-Stage Startups

Product-Led Growth (PLG) and content marketing are particularly valuable for startups in their initial stages. Here's why:

Product-Led Growth

PLG puts the product at the forefront of customer acquisition and retention. It allows users to experience value before committing to a purchase, often through freemium models or free trials. This approach:

  • Reduces customer acquisition costs
  • Accelerates user adoption
  • Drives organic word-of-mouth growth

Content Marketing

Content marketing establishes thought leadership and builds trust with potential customers. It:

  • Attracts and educates prospects
  • Improves SEO, driving organic traffic
  • Provides value throughout the customer journey

Both PLG and content marketing create sustainable, scalable growth engines that can fuel a startup's journey to significant revenue milestones.

High-Growth Success Stories

Many SaaS companies have leveraged these growth channels to reach $100M+ ARR:

  1. Slack: Used PLG to grow from $0 to $100M ARR in just 3 years.
  2. HubSpot: Built a content marketing empire, becoming a go-to resource for inbound marketing.
  3. Dropbox: Combined PLG with a viral referral program to achieve rapid user acquisition.
  4. Zoom: Utilized a freemium model and word-of-mouth marketing to dominate the video conferencing market.

These success stories demonstrate how effective PLG and content marketing can be in creating a strong foundation for future growth, often complemented by other channels as the company scales.


https://bit.ly/46U1jHU
https://bit.ly/3yGDgj5

https://guptadeepak.com/content/images/2024/08/Screenshot-2024-08-15-at-2.04.23-PM.png
https://guptadeepak.weebly.com/deepak-gupta/fuel-your-b2b-saas-startups-growth-6-essential-channels

Wednesday, 14 August 2024

The Future of Search: AI-Powered Transformation

The Future of Search: AI-Powered Transformation

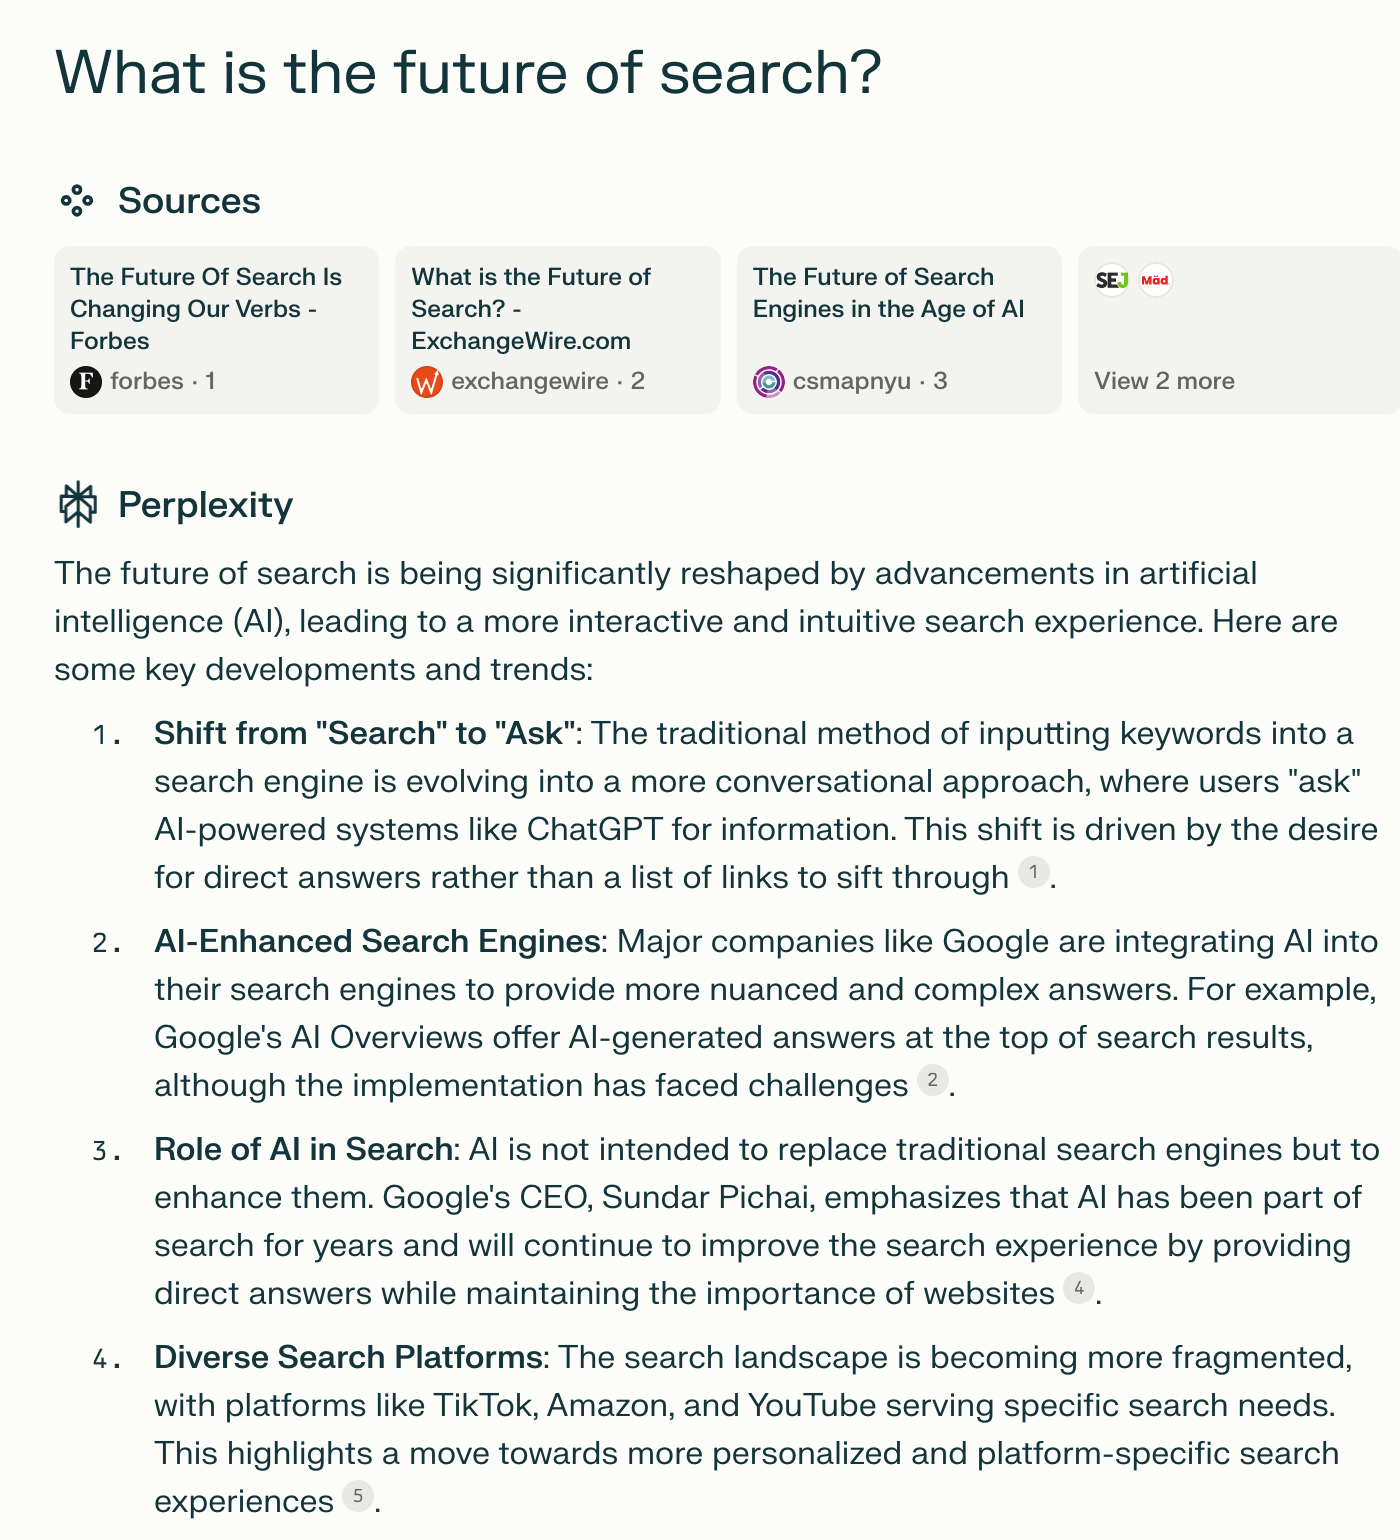
In the rapidly evolving landscape of artificial intelligence, traditional marketing playbooks are quickly becoming obsolete. As AI chatbots like ChatGPT, Perplexity and Exa reshape how consumers search for and interact with information, businesses must adapt their growth strategies to remain relevant and competitive.

The Shifting Search Paradigm

The rise of AI-powered search assistants marks a significant departure from conventional search engine optimization (SEO) tactics. Users are increasingly turning to conversational AI interfaces for quick, personalized answers, bypassing traditional search engine results pages. This shift necessitates a fundamental rethinking of how brands approach visibility and discoverability.

  1. Natural Language Queries: AI systems excel at understanding and responding to conversational, human-like questions, moving away from keyword-based searches.
  2. Intent Recognition: Advanced AI can better interpret the user's underlying intent, providing more accurate and relevant results.
  3. Personalized Results: AI-powered search takes into account user history, preferences, and context to deliver highly personalized results.
  4. Real-time Information Synthesis: Instead of simply returning links, AI can synthesize information from multiple sources to provide comprehensive answers.
  5. Multi-modal Search: AI is enabling more sophisticated image and voice searches, expanding beyond text-based queries.

AI Evaluation of Website Trustworthiness

AI systems are becoming increasingly sophisticated in evaluating the trustworthiness and relevance of websites, especially when it comes to specific products:

  1. Content Quality Assessment: AI analyzes the depth, accuracy, and uniqueness of content, favoring well-researched, original information.
  2. User Engagement Metrics: AI considers factors like time spent on site, bounce rates, and user interactions to gauge content value.
  3. Backlink Analysis: The quality and relevance of backlinks remain important, with AI better able to discern natural link patterns from artificial ones.
  4. Brand Authority: AI systems recognize established brands and authoritative voices in specific industries.
  5. Data Consistency: Consistent information across multiple trusted sources increases a website's credibility in AI evaluations.
  6. User Reviews and Sentiment: AI analyzes user reviews and overall sentiment across various platforms to assess product and brand reliability.
  7. Technical Performance: Website speed, mobile-friendliness, and overall user experience factor into AI trustworthiness assessments.

Reinventing Marketing for AI

To thrive in this new era, companies must:

  1. Optimize for Conversational AI: Develop content that aligns with the natural language processing capabilities of AI chatbots. This means focusing on clear, concise, and informative content that directly addresses user queries.
  2. Prioritize Brand Authority: As AI systems often prioritize reputable sources, establishing your brand as a thought leader in your industry becomes crucial. Invest in creating high-quality, authoritative content that AI is likely to reference.
  3. Embrace AI-Powered Analytics: Utilize AI tools to gain deeper insights into customer behavior and preferences, allowing for more targeted and effective marketing strategies.
  4. Personalization at Scale: Leverage AI to deliver hyper-personalized experiences to customers, enhancing engagement and loyalty.
  5. Ethical AI Integration: Incorporate AI into your marketing efforts responsibly, ensuring transparency and maintaining consumer trust.
  6. Structured Data Implementation: Use schema markup and other structured data formats to help AI systems better understand and categorize your content.
  7. Voice Search Optimization: Adapt content for voice search queries, which are often longer and more conversational than text-based searches.

Redefining Brand Value

In an AI-driven world, brand value extends beyond traditional metrics. Companies must now consider:

  • AI Compatibility: How easily can your brand be understood and recommended by AI systems?
  • Data Quality: The accuracy and relevance of your digital footprint will directly impact AI-driven recommendations.
  • User Experience: Seamless integration between AI interfaces and your brand's digital presence is crucial.
  • Trust Signals: Implement clear trust signals (certifications, transparent policies, expert endorsements) that AI can recognize and value.
  • Cross-platform Consistency: Maintain consistent brand messaging and information across all digital platforms to reinforce credibility to AI systems.

Conclusion

The AI revolution demands a radical reimagining of marketing and growth strategies. By embracing these changes and innovating accordingly, brands can not only survive but thrive in this new era. The key lies in adaptability, authenticity, and a willingness to explore the uncharted territories of AI-driven marketing. As AI continues to evolve, so too must our approaches to building and maintaining brand value in this dynamic digital landscape.


https://bit.ly/3SQRe8V
https://bit.ly/3M5WGkp

https://guptadeepak.com/content/images/2024/08/Screenshot-2024-08-14-at-12.02.22-PM.png
https://guptadeepak.weebly.com/deepak-gupta/the-future-of-search-ai-powered-transformation

Monday, 5 August 2024

Human vs AI Agents in Cybersecurity: Who Should Guard Your Data?

Human vs AI Agents in Cybersecurity: Who Should Guard Your Data?

In the ever-evolving landscape of cybersecurity, we face a pivotal question: Should we entrust the protection of our most valuable data to human experts or artificial intelligence (AI) agents? As cyber threats become increasingly sophisticated, this decision carries more weight than ever. Let's dive into this complex issue, exploring how AI agents might just be the guardians we need in the digital age.

The Human Touch: A Double-Edged Sword

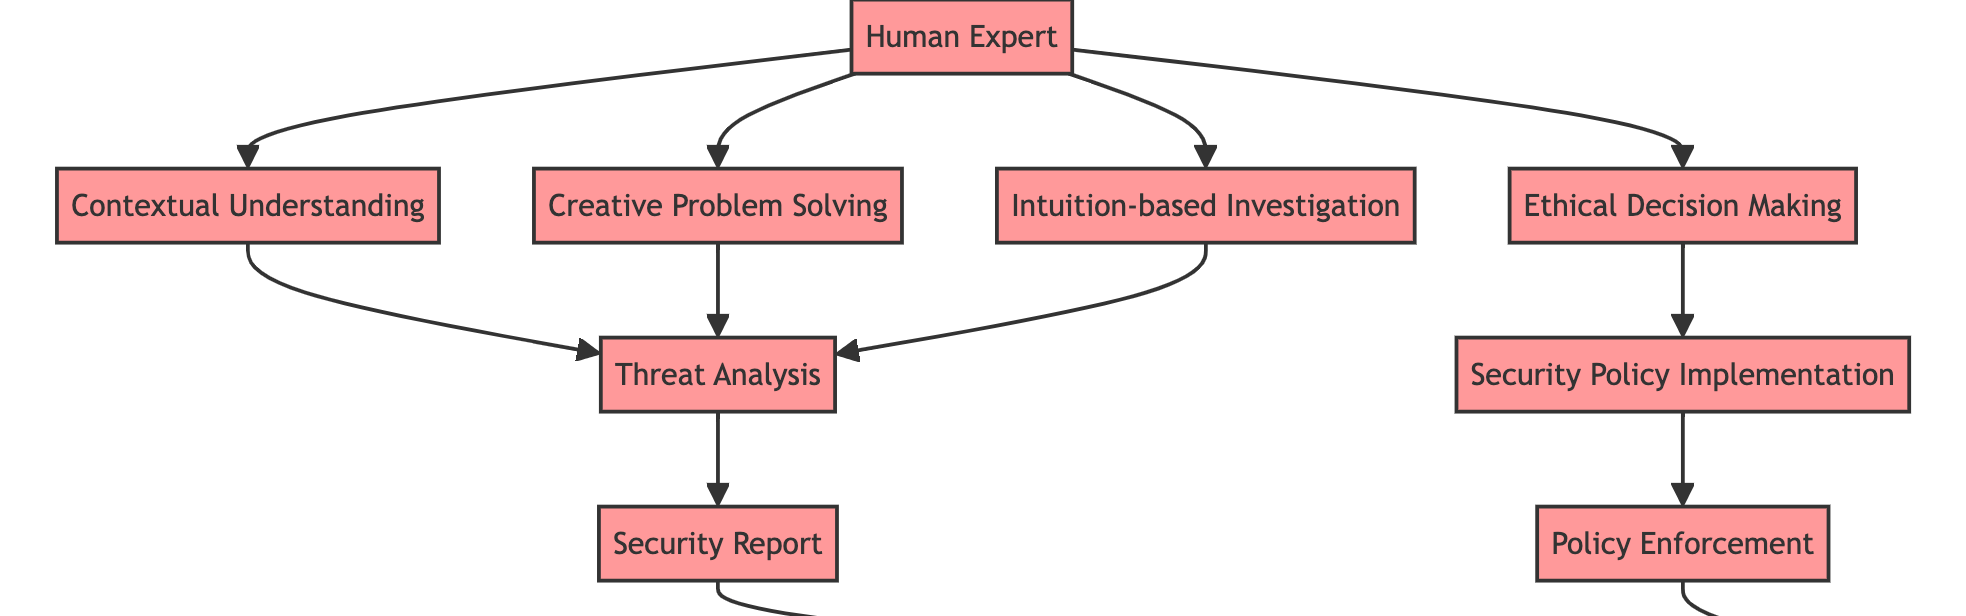
Humans have been at the forefront of cybersecurity since its inception. We've relied on the intuition, creativity, and adaptability of skilled professionals to defend against cyber threats. Human cybersecurity experts bring invaluable traits:

  1. Contextual understanding
  2. Ethical decision-making
  3. Creative problem-solving
  4. Emotional intelligence in crisis management

However, human involvement also introduces vulnerabilities:

  1. Fatigue and burnout
  2. Unconscious biases
  3. Limited processing speed
  4. Inconsistency in performance

As cyber attacks increase in frequency and complexity, these human limitations become more pronounced. This is where AI agents enter the picture, offering a compelling alternative.

AI Agents: The Tireless Guardians

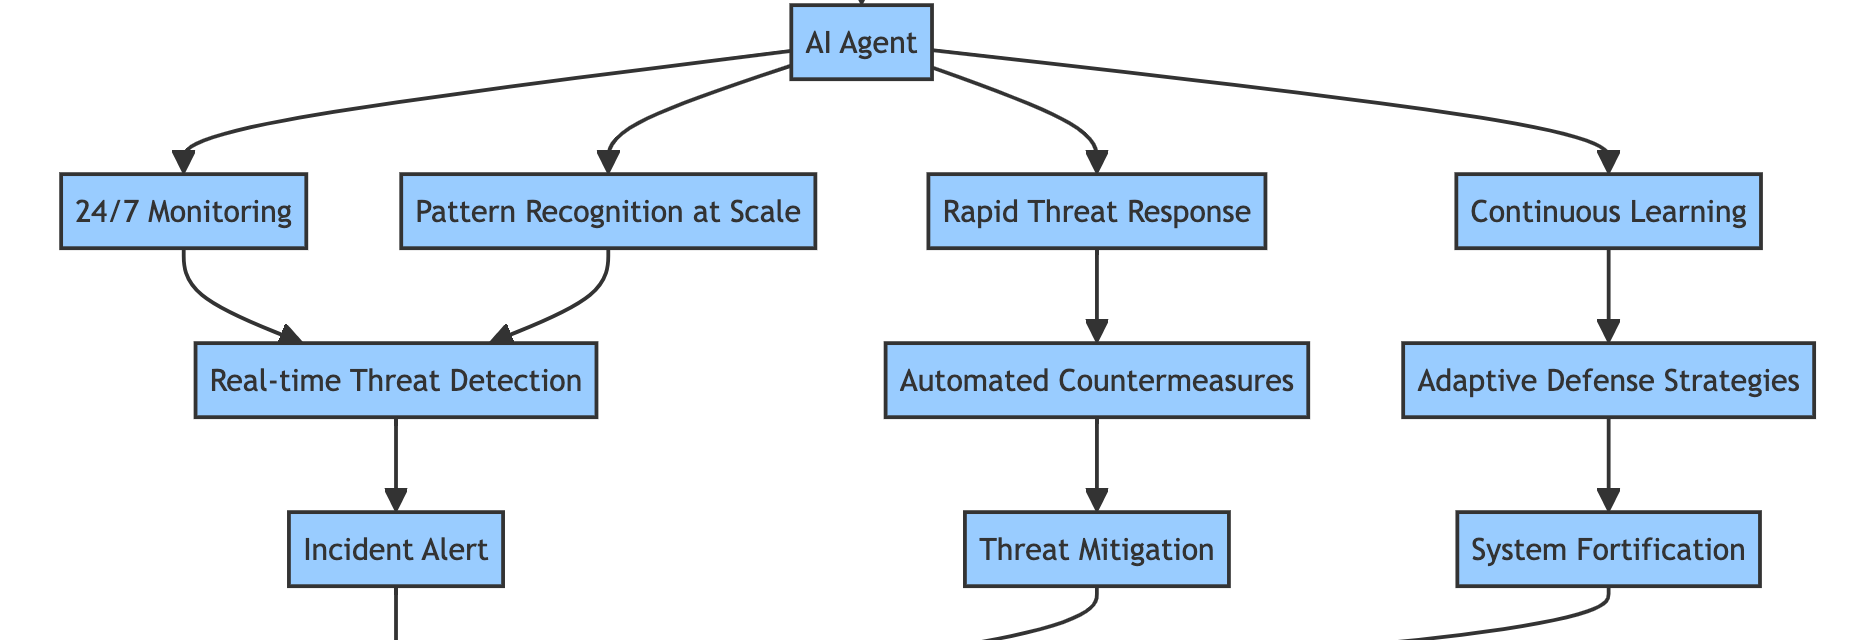
AI agents in cybersecurity are not just tools; they're evolving into autonomous defenders capable of learning, adapting, and making decisions at machine speed. Here's how they're changing the game:

1. Constant Vigilance

Unlike humans, AI agents don't need sleep. They can monitor networks 24/7, analyzing vast amounts of data in real-time. Imagine an AI agent "Argus":

Argus tirelessly scans millions of data points per second across your network. At 3:27 AM, it detects an unusual pattern of encrypted traffic from a database server. Within milliseconds, it correlates this with recent threat intelligence, identifies it as a potential data exfiltration attempt, and initiates countermeasures – all before a human analyst would have even logged in for their morning coffee.

2. Pattern Recognition at Scale

AI excels at identifying patterns in vast datasets, a crucial ability in detecting novel cyber threats. Consider an AI system "Sherlock":

Sherlock analyzes billions of network transactions across thousands of organizations. It notices a subtle commonality in seemingly unrelated phishing attempts targeting different industries. This pattern is so nuanced that it would have taken human analysts months to connect the dots. Sherlock immediately updates threat signatures across all protected networks, effectively inoculating them against this new attack vector.

3. Rapid Adaptation to New Threats

In the arms race of cybersecurity, speed is critical. AI agents can learn and adapt to new threats faster than any human team. Let's introduce "Phoenix":

Phoenix, an AI-driven intrusion prevention system, encounters a previously unseen type of malware. It quickly analyzes the malware's behavior, creates a signature, and deploys a countermeasure. Phoenix then simulates thousands of variations of this malware, predicting potential mutations. By the time the malware authors release their next version, Phoenix is already ten steps ahead, with defenses in place for hundreds of possible variants.

4. Unbiased Decision Making

AI agents make decisions based on data, free from human biases that can cloud judgment. Meet "Themis":

Themis, an AI security policy enforcer, notices that a C-level executive's account is exhibiting suspicious behavior indicative of a compromise. Unlike a human analyst who might hesitate due to the executive's status, Themis impartially applies security protocols, temporarily restricting the account's privileges and initiating a thorough investigation, potentially stopping a major breach in its tracks.

Learning from Experience: The AI Advantage

One of the most powerful aspects of AI in cybersecurity is its ability to learn from every interaction, attack, and defense. This continuous learning process creates a feedback loop that constantly improves the AI's capabilities.

Imagine an AI agent called "Hydra":

Hydra defends against a sophisticated attack on a financial institution. Although it successfully prevents data theft, the attackers manage to briefly disrupt services. Hydra analyzes every millisecond of the attack, identifying minute weaknesses in its response. It then runs millions of simulations, refining its strategies. The next time a similar attack occurs, Hydra's response is orders of magnitude more effective. Unlike a human team, which might take months to implement lessons learned, Hydra's improvements are immediate and continuously compounding.

The Symbiosis of Human and AI in Cybersecurity

While AI agents offer compelling advantages, the ideal scenario isn't an either/or choice between humans and AI. Instead, the future of cybersecurity lies in a symbiotic relationship between human experts and AI agents.

Humans provide the strategic oversight, ethical boundaries, and creative thinking that guide AI systems. They ask the right questions, set the priorities, and make the high-level decisions that shape cybersecurity policies.

Human vs AI Agents in Cybersecurity: Who Should Guard Your Data?

AI agents, in turn, handle the heavy lifting of data analysis, pattern recognition, and real-time threat response. They augment human capabilities, allowing cybersecurity teams to operate at unprecedented scales of speed and efficiency.

Together, they form a cybersecurity ecosystem that's greater than the sum of its parts. Humans and AI agents working in concert can create adaptive, intelligent defense systems capable of protecting our most valuable data in an increasingly complex digital world.

Embracing the AI Guardian

As we stand at this technological crossroads, the question isn't really whether we want humans or AI agents protecting our valuable data. The question is: How quickly can we integrate AI agents into our cybersecurity strategies to create more robust, responsive, and intelligent defense systems?

The cyber threats of tomorrow will be faster, more complex, and more devastating than ever before. To meet this challenge, we need guardians that can operate at the speed of data, learn from every encounter, and adapt in real-time. AI agents, working alongside human experts, offer our best hope for securing our digital future.

In the end, the choice to embrace AI in cybersecurity isn't just about protecting data – it's about staying one step ahead in a rapidly evolving digital landscape. As we entrust more of our lives and societies to digital systems, having AI guardians at the gate isn't just an option – it's becoming a necessity.


https://bit.ly/46xmQ9d
https://bit.ly/4fzpz5T

https://guptadeepak.com/content/images/2024/08/Screenshot-2024-08-05-at-1.34.35-PM.png
https://guptadeepak.weebly.com/deepak-gupta/human-vs-ai-agents-in-cybersecurity-who-should-guard-your-data

Palo Alto Networks CyberArk: The $25 Billion Deal Reshaping Cybersecurity

Deal Overview Transaction Details : Palo Alto Networks announced on July 30, 2025, its agreement to acquire CyberArk for $45.00 in cash...